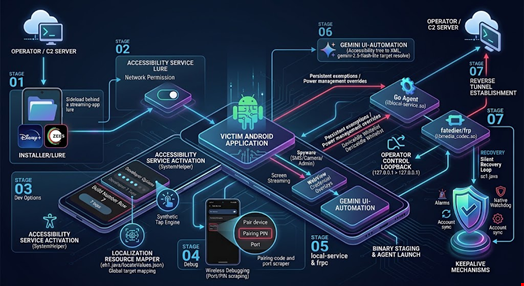
RatHat Android malware uses a generative AI assistant to steal banking credentials
Ourtake
Malware that takes navigation decisions from a generative AI model is harder for signature-based mobile defenses to catch.
What happened
Zimperium researchers identified RatHat, a new Android malware strain linked to threat actors believed to operate in China. It spreads through smishing, malvertising and fake apps, steals banking credentials, 2FA and OTP keys, and uses a generative AI assistant to interpret screen data and direct clicks.