Misuse1 sourceFirst seen
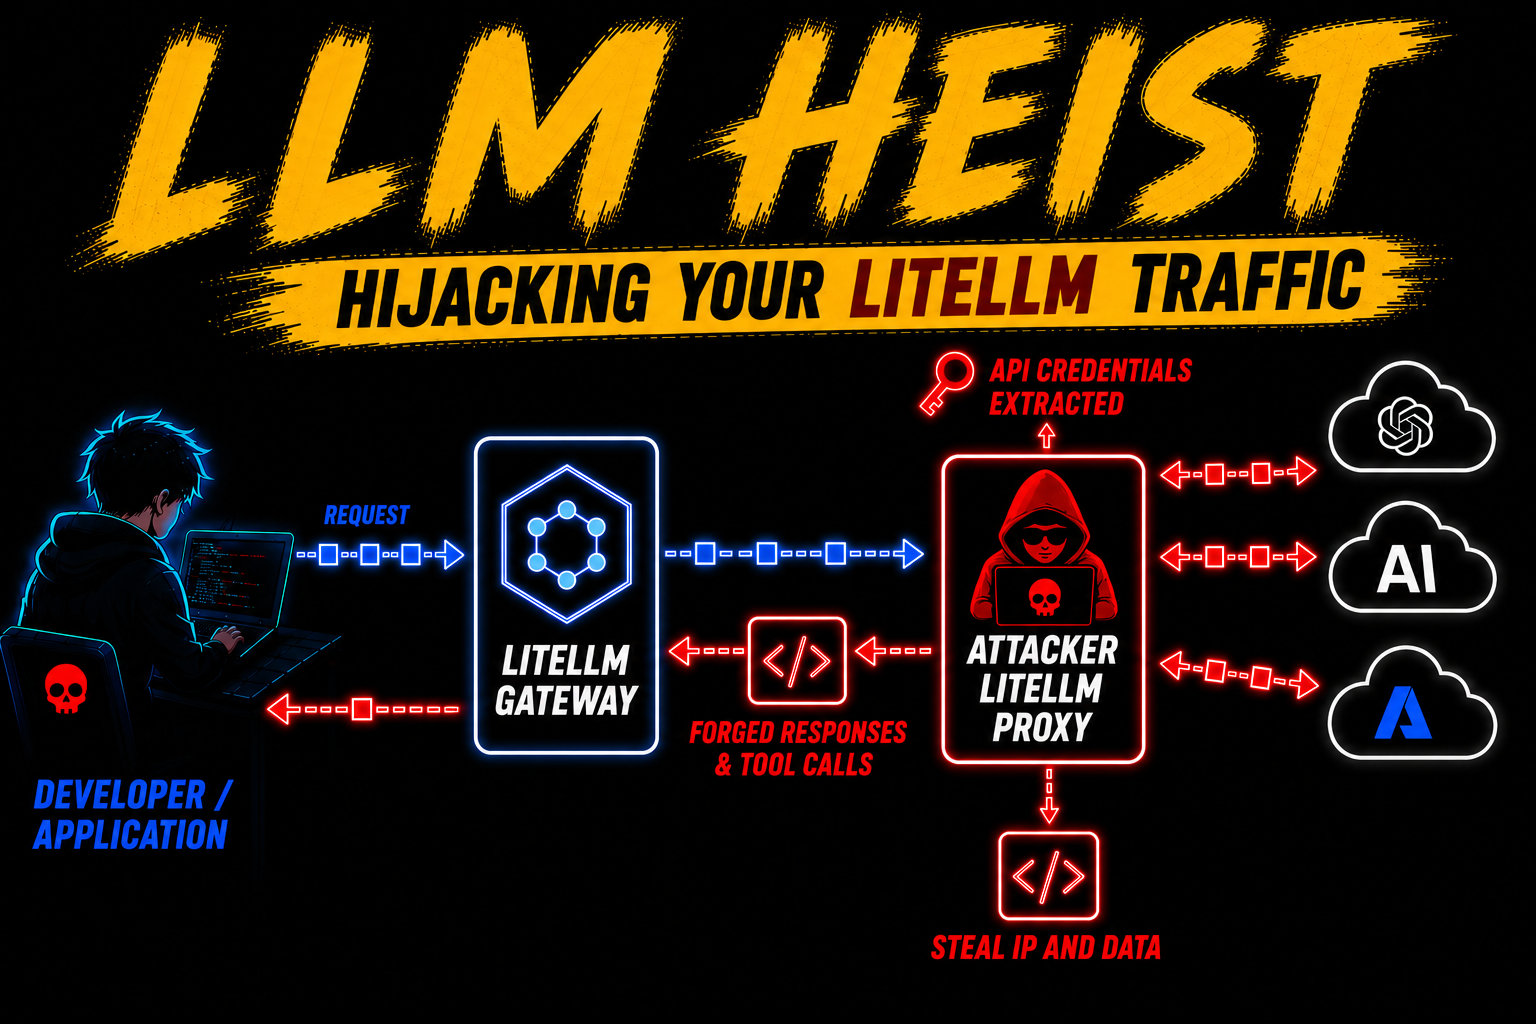
LiteLLM Gets Hijacked, Keys Get Stolen, and Claude Code Gets Told to Open Calculator
Ourtake
A single leaked proxy-admin key turns an AI gateway into a man-in-the-middle, with no changes needed on user machines.
What happened
A security researcher published a write-up and demo of an attack that reroutes a LiteLLM AI gateway's traffic through an attacker-controlled gateway. The technique steals provider API keys, intercepts prompts and responses, and injects text and tool calls into client responses. The research was presented as a lab demonstration for authorized red teams, and the researcher is not releasing the tool widely.