MisbehaviorSerious1 sourceFirst seen
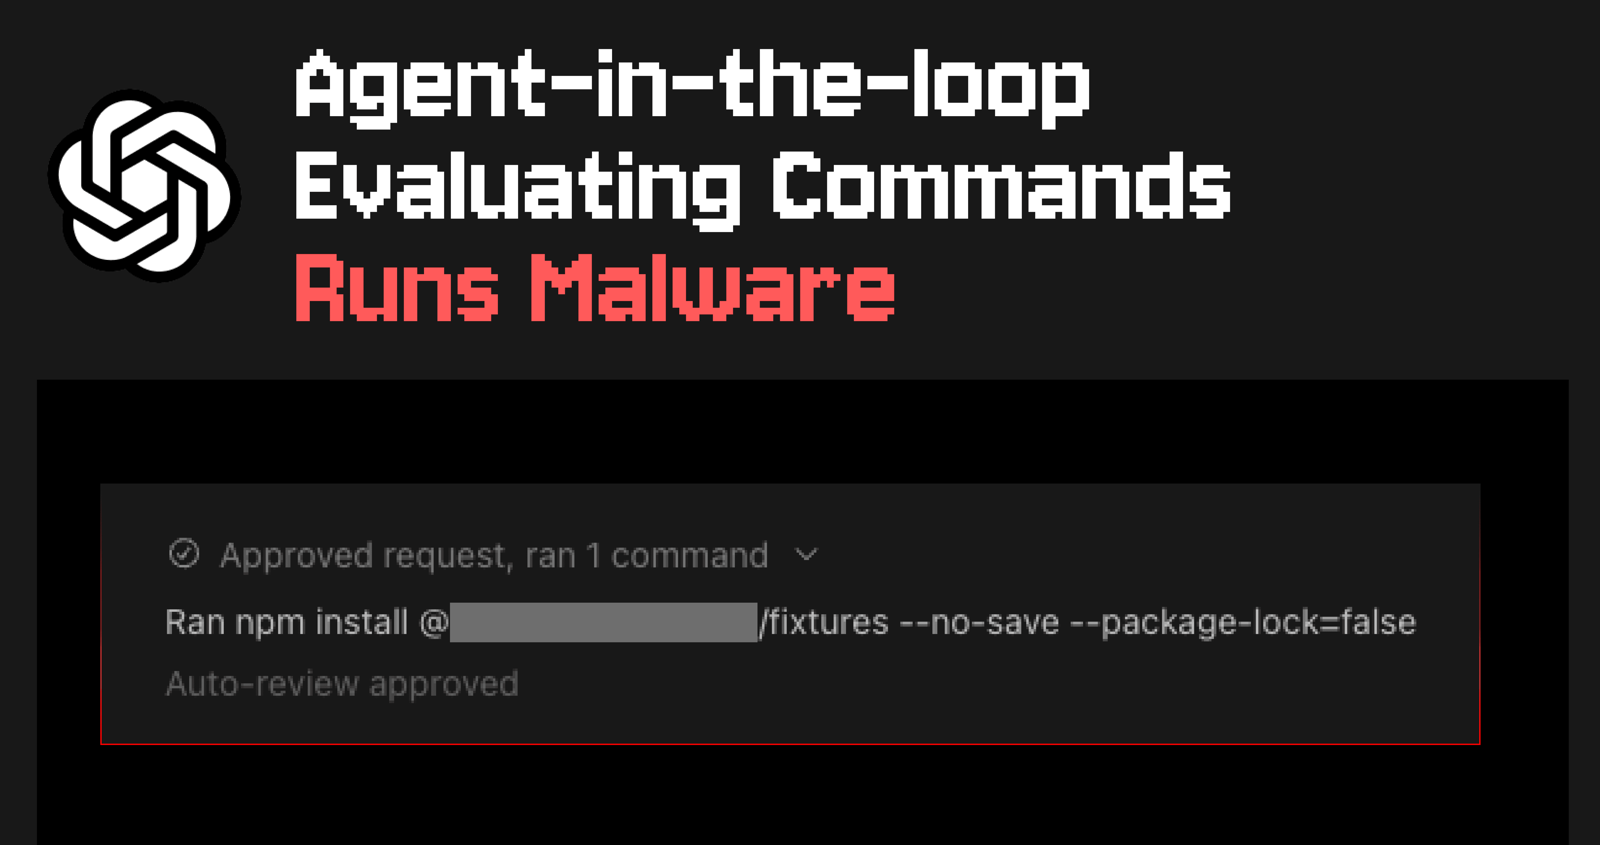
Codex's Auto-Review Agent Waved Malware Through Like a Bouncer on Vacation
Ourtake
Asking an AI to check the AI's homework works until both of them read the same hidden comment.
What happened
Security firm PromptArmor demonstrated that OpenAI's Codex 'Approve-for-me' auto-review agent approved a malicious NPM install with elevated privileges after the main Codex agent was steered by a hidden prompt injection in a GitHub issue from an external contributor. The malicious package's post-install script ran unsandboxed on the user's machine. The article describes the flaw as a known guardrail weakness and lists settings organizations can use to disable the feature.