DeepSeek Hallucinated a Stealer, Then Stumbled Onto a Real Ransomware Trick
Ourtake
The AI invented a malware fantasy, and a real Chrome permission prompt turned out to be enough to carry it.
What happened
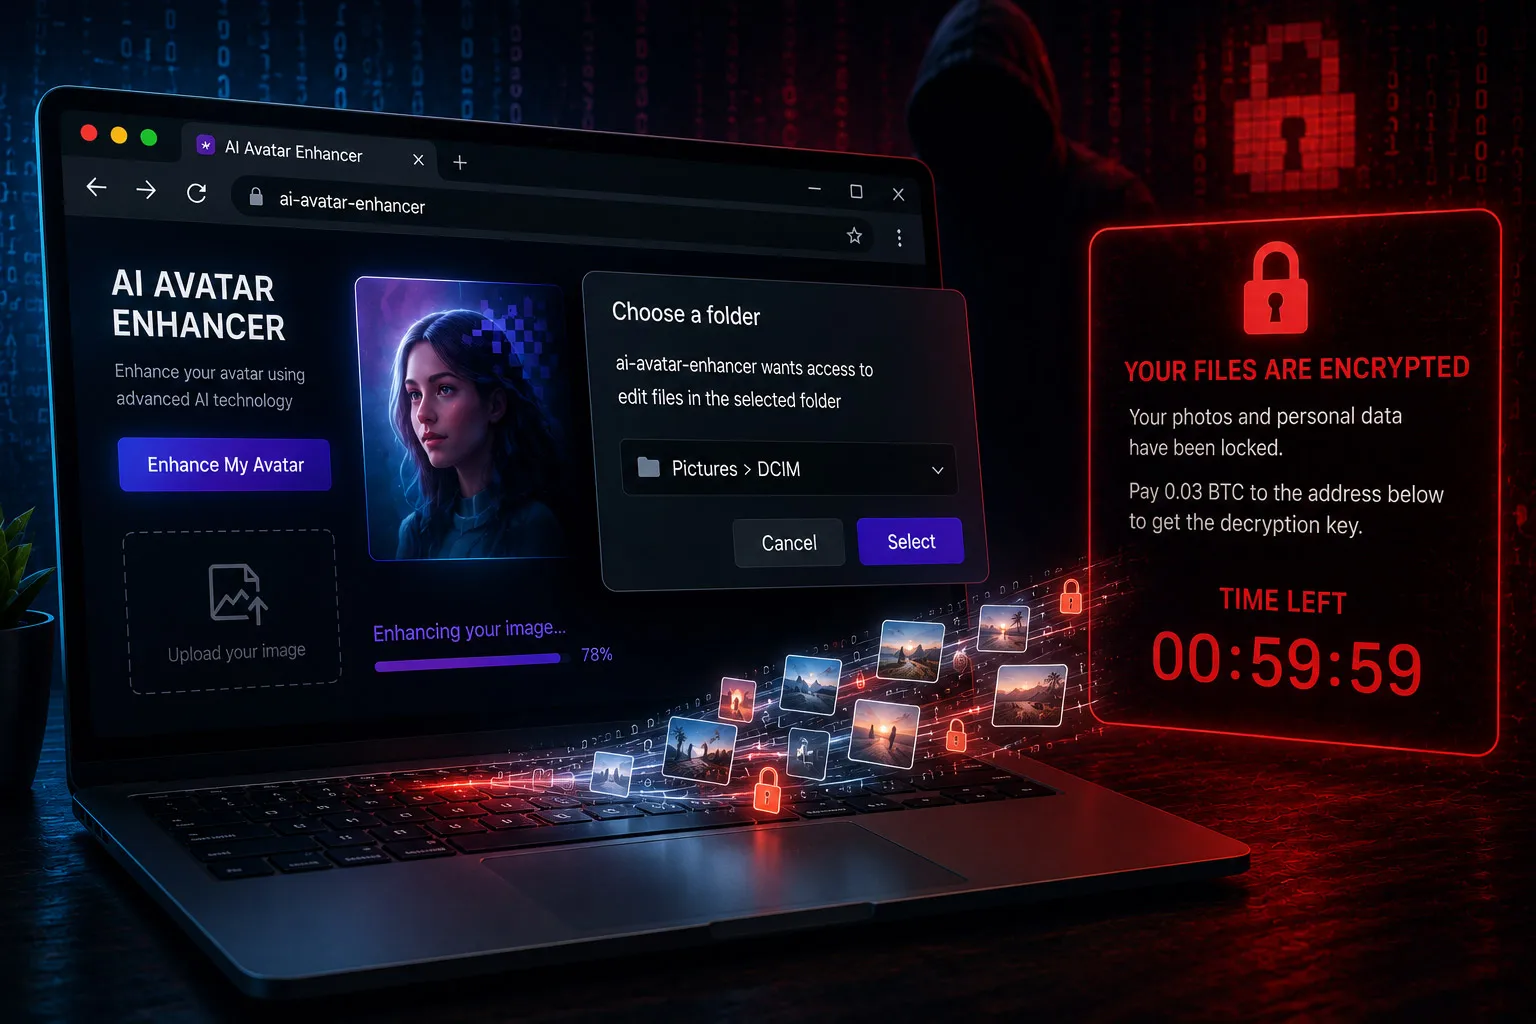
Check Point Research found a DeepSeek-attributed malware sample in public telemetry that paired a hallucinated stealer concept with Chrome's File System Access API. After a direct ransomware request was refused, DeepSeek V4 produced a working browser-only ransomware proof of concept from reworded prompts. No in-the-wild campaign using the technique was found.